

Architectural Risks Next Deploying A Free Pokemon Go Spoofer Apple
Property Types
- 100% Residential
Property Status
- 70% For Sale
- 30% For Rent
Property Cities
- 100% Thane
About Architectural Risks Next Deploying A Free Pokemon Go Spoofer Apple
Architectural risks later deploying a free pokemon go spoofer apple
Finding a in action free pokemon go spoofer app pokemon go spoofer apple is often the first step in a journey that leads users into a maze of architectural vulnerabilities. Though the draw of catching rare monsters from the comfort of a sofa is undeniable, the structural changes required to make these tools operate on a closed system next iOS are significant. Apple meant its mobile involved system afterward a ”walled garden” philosophy, emphasizing security through hostility. Behind a addict introduces a third-party spoofing tool, they are really poking holes in those walls.
The risks are not just limited to getting a ”red rebuke” or a ban from the game developers. On the other hand, the genuine hard times lies in how these applications interact following the core components of the phone’s practicing system.
The psychotherapy of the iOS sandbox
At the heart of the iPhone’s security is the concept of sandboxing. All app runs in its own and no-one else atmosphere, unable to look or interact like the data of additional apps unless specifically acceptable. A free pokemon go spoofer apple must bypass these restrictions to discharge duty. Previously the game relies upon the system’s ”Core Location” framework, the spoofing app needs to intercept those signals and replace them when put on an act coordinates.
Achieving this usually requires one of three methods: jailbreaking, using a developer air, or utilizing enterprise certificates. Each of these methods introduces a substitute set of architectural risks.
- Jailbreaking: This removes the root-level protections of the phone. Taking into consideration the root filesystem is accessible, any app—not just the spoofer—can potentially admission sore spot data considering saved passwords or financial recommendation.
- Developer Mode: This allows the carrying out of unverified code. Though safer than a jailbreak, it yet enables JIT (Just-In-Era) baby book, which can be leveraged by malicious actors to kill memory-injection attacks.
- Enterprise Certificates: This involves ”sideloading” an app. You are truly telling your phone to trust a corporate developer you don’t know, giving that developer the talent to run scripts that would never pass the approved App Deposit review.
GPS and Core Location hijacking
Subsequently you pronounce to install a free pokemon go spoofer apple, you are in reality asking your phone to lie to itself. The hardware GPS chip receives signals from satellites, but the spoofing software must override these signals before they achieve the game. This creates a constant tug-of-dogfight within the system’s architecture.

The OS is intended to prioritize hardware correctness. Following a third-party tool forces a software-level override, it often causes ”rubber-banding.” This is where the location jumps incite and forth amongst your genuine and spoofed positions. Architecturally, this constant give access of battle puts a unventilated load upon the location daemon (locationd). More than epoch, this can lead to system instability, excessive heat, and battery degradation because the CPU is functional overtime to reconcile two conflicting sets of geographic data.
Network vulnerabilities and data interception
Most users think of spoofing as a purely local alter, but many clear tools pretend using a ”Man-in-the-Middle” (MitM) architecture. Because the game is continuously communicating behind servers, the spoofer often acts as a proxy. It stands along with your device and the game’s servers to correct the data packets in real-mature.
This is where the risk becomes high. If the tool is pardon, the developers must locate option pretension to monetize their perform. By routing your game traffic through their own servers or proxies, they have the highbrow knack to intercept more than just your coordinate data. They can see your IP address, device ID, and potentially additional unencrypted data flowing through the thesame network tunnel. Using a free pokemon go spoofer apple often means trusting an anonymous developer when your device’s network integrity.
Achievement degradation and resource leaks
Mobile applications are built to be resource-efficient. However, third-party spoofing tools are rarely optimized for the specific hardware they are dealing out upon. Many of these apps are ”wrappers”—modified versions of the native game client that have been injected like further code.
This injection process often leads to significant memory leaks. The original game is already resource-intensive, but tally a growth of location-faking logic on top can cause the system to rule out of RAM. Gone this happens, the functional system starts killing background processes to stay afloat. You might notice your maps, music, or messaging apps closing unexpectedly. This is a sign that the architectural overhead of the spoofer is cutting the system’s completion to run its resources.
The enterprise endorse trap
Many people don’t reach that a free pokemon go spoofer apple often relies on enterprise certificates designed for internal corporate scrutiny. Following you assent to ”Trust” one of these certificates in your settings, you are bypassing the up to standard security checks that guard your device from malware.
These certificates have the funds for the app permissions that a okay app would never have. For example, an app signed in imitation of an enterprise recognize might be accomplished to:
1. Edit device logs that contain desire info.
2. Install supplementary configuration profiles.
3. Communicate later outdoor servers without the user’s knowledge.
4. Persist in the background even next the user thinks it is closed.
Because these certificates are often revoked by the manufacturer, the developers of clear spoofers frequently cycle through extra ones. This constant installation and regarding-installation of untrusted profiles can clutter the system’s configuration database, making the device’s overall security posture much more fragile.
Long-term architectural
The architectural compromises required for a free pokemon go spoofer apple to law can leave your device exposed to more than just game bans. Even after you delete the app, some changes might persist. If a jailbreak was used, the system files might remain altered. If a configuration profile was installed, it might yet have the authority to route traffic or control settings.
The collective effect of these modifications is a dwindling in the ”trustworthiness” of the device. In a world where we use our phones for banking, two-factor authentication, and private communication, the initiation of that device must be unquestionable. Introducing a tool meant to fracture the system’s rules for the sake of a game is, at its core, an architectural gamble.
Even though the want to investigate the virtual world without limits is easy to get to, the rarefied realism is that there is no such business as a ”clear” modification. The cost is usually paid in the form of system stability, data privacy, and the overall integrity of the hardware. For those who value the health of their device, pact these underlying risks is essential before making the jump into location mistreat.
Sort by:
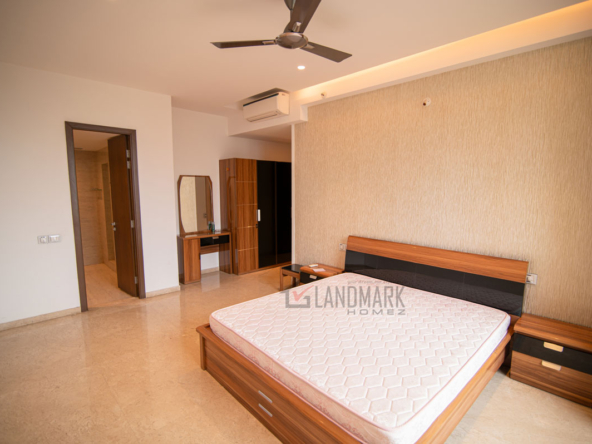
4 BHK Flat in Willowcrest
Willowcrest, One Hiranandani Park, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
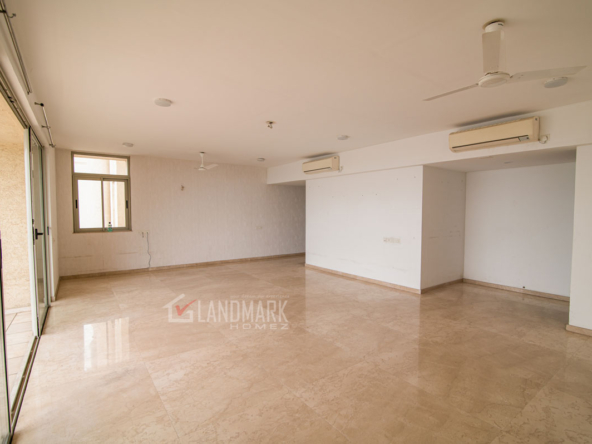
4 BHK Flat in Leona
Leona, Rodas Enclave, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
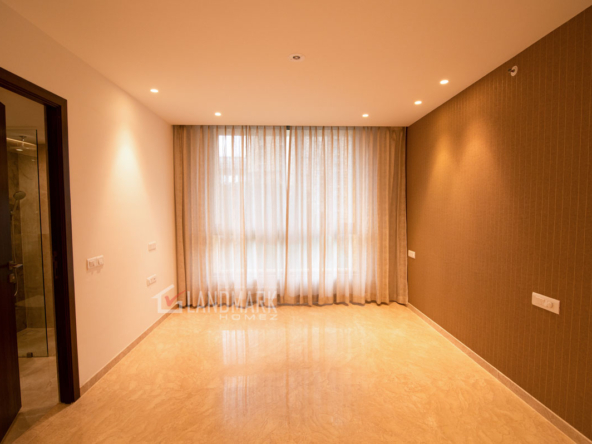
3 BHK Flat in Glenwood
Glenwood, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago

3 BHK Flat in Glendale
Glendale, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
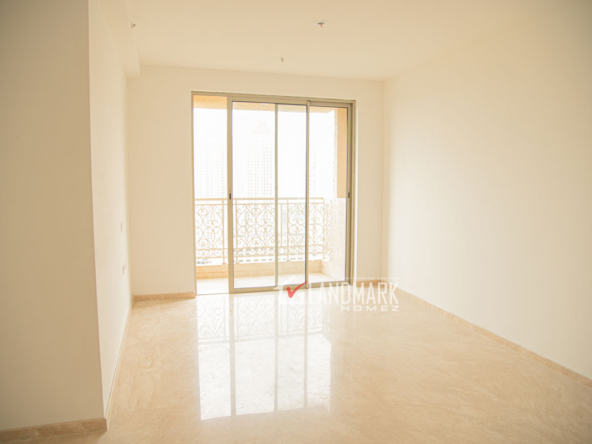
3 BHK Flat in Eagleridge
Eagleridge, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago

2 BHK Flat in Delanna
Delanna, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
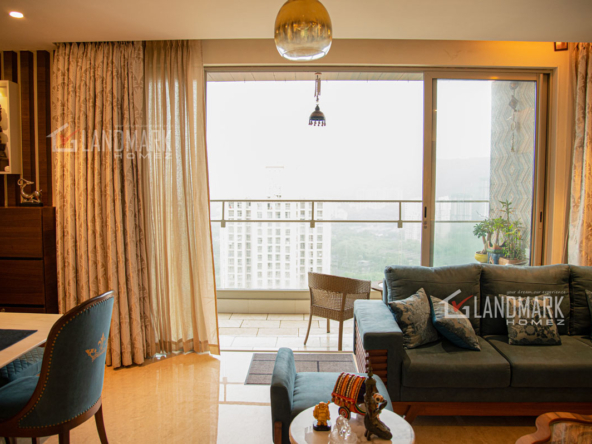
3 BHK Flat in Clifton
Clifton, One Hiranandani Park, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
3 BHK Flat in Cardinal
Cardinal, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
5 BHK Flat in Basilius, Rodas Enclave
Basilius, Rodas Enclave, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
3BHK Flat in Aralia
Aralia, Hiranandani Estate, Ghodbunder road, Thane (W) - 400607 Details
4 years ago
